authPRIME
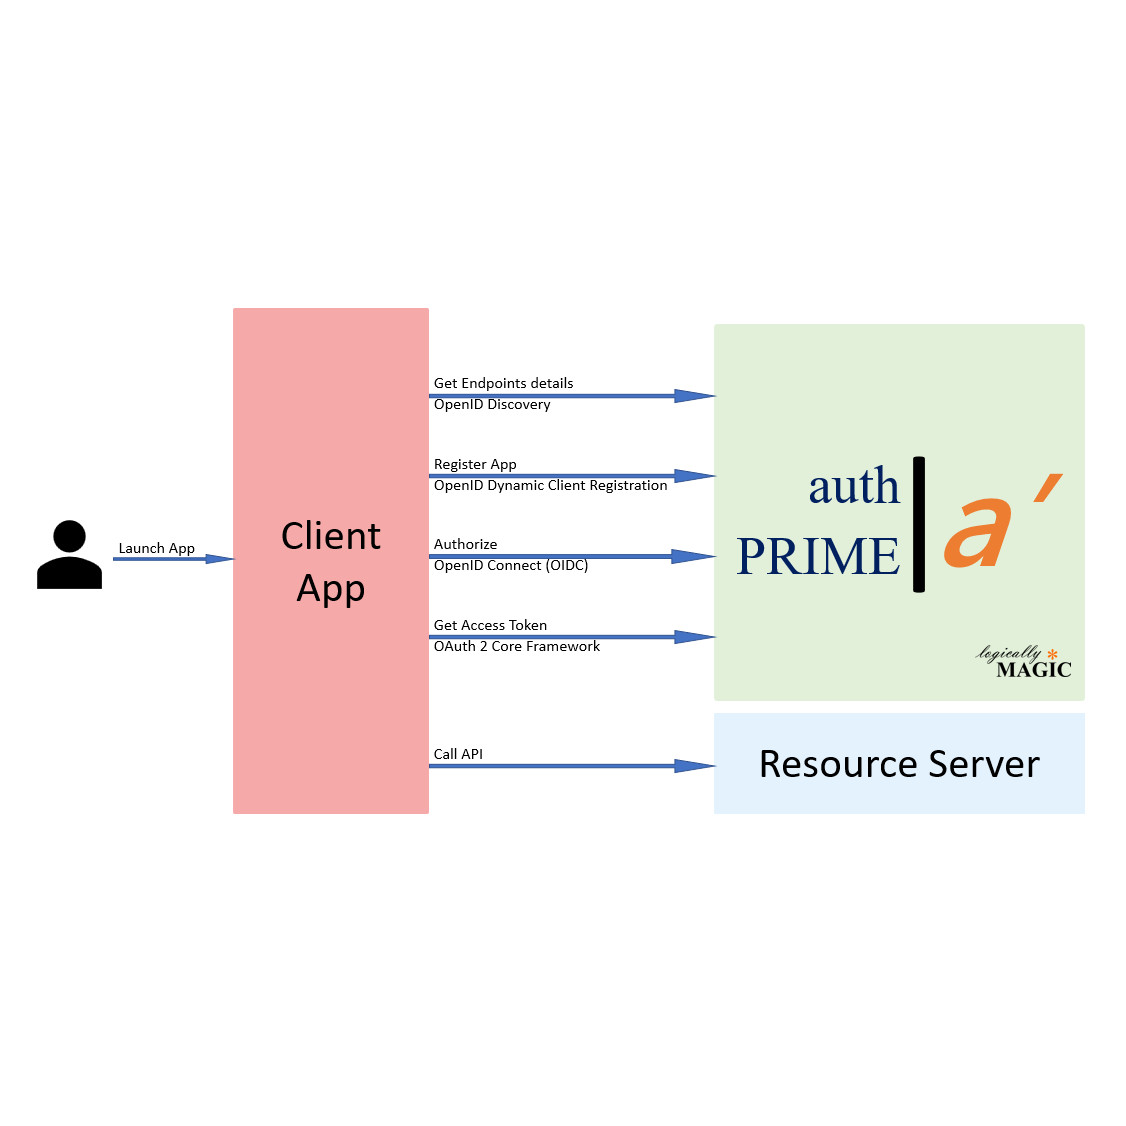
authPRIME is an OAuth 2.0 Authorization Server with support for OpenID Connect (OIDC), FAPI 1 / FAPI 2 profiles, and many other additional features and standards.
The business case
- Identity is the front door to every product. Getting it wrong is front-page news; getting it right is invisible. authPRIME implements the full modern standards stack so your front door is boring in the best way.
- FAPI profiles open the regulated market. Financial-grade API (FAPI 1 and FAPI 2) conformance is what banks and regulators expect from open banking and payments integrations. authPRIME ships with it — this is the same engine behind our Open Banking platform.
- Dynamic client registration scales partnerships. Partners onboard themselves through the standard DCR flow instead of an e-mail thread with your security team.
- Every logout and revocation edge case, covered. RP-initiated logout, back-channel logout, and token revocation are the details that decide whether an identity deployment survives a security review.
Standards implemented
- RFC 6749 — OAuth 2.0 & OIDC Core 1.0
- OIDC Discovery 1.0
- Dynamic Client Registration
- OIDC RP-Initiated Logout 1.0
- OIDC Back-Channel Logout 1.0
- RFC 7009 — OAuth 2.0 Token Revocation
- RFC 7636 — Proof Key for Code Exchange (PKCE)
- RFC 7662 — OAuth 2.0 Token Introspection
- RFC 8252 — OAuth 2.0 for Native Apps BCP (AppAuth)
- RFC 8628 — OAuth 2.0 Device Authorization Grant
- FAPI 1 / FAPI 2 profiles
Who it's for
- Fintechs and banks needing an FAPI-conformant authorization server.
- Enterprises replacing legacy SSO with a standards-complete OIDC provider.
- Platform companies issuing identity to partner ecosystems via dynamic client registration.